Scammers are spreading fake Claude installers loaded with malware
Scammers are cloning Claude's website and offering fake installers instead of the real app. Users think they are installing an AI assistant, but they get malware. How can you avoid it? Look for typos in the domain name, poor Russian translation, and links that come from spam or social media.
AI-processed from Habr AI; edited by Hamidun News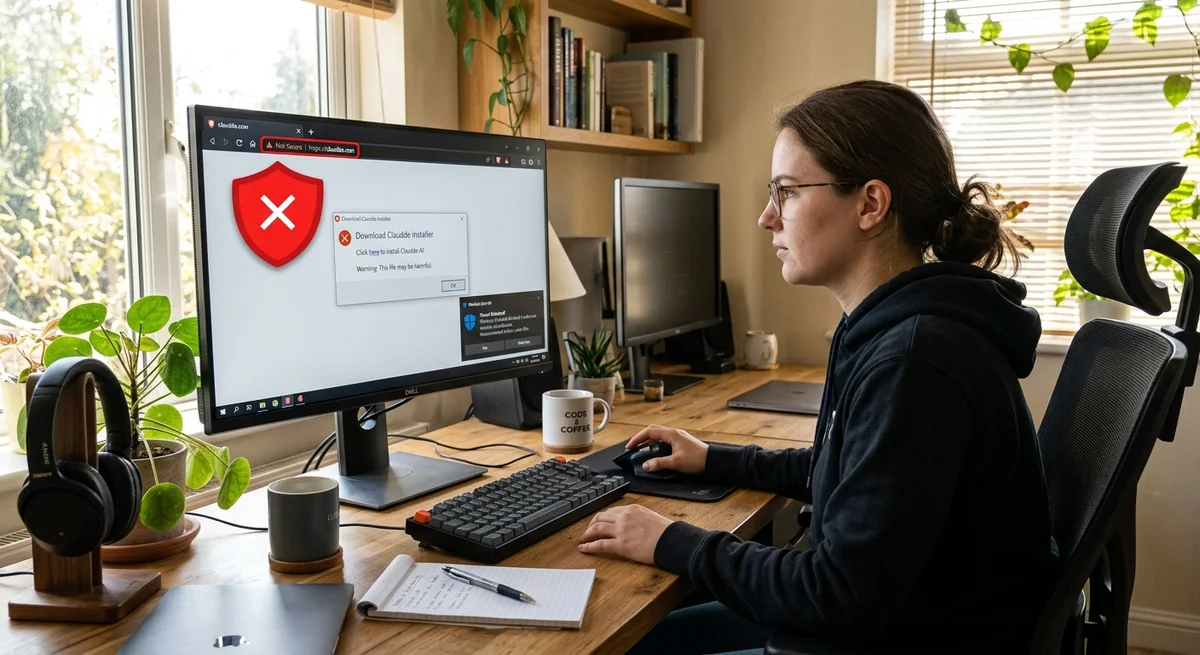
There is a new trend on the dark side of the internet: scammers are building fake websites for Claude, ChatGPT and other popular AI tools, then distributing malicious "installers" through spam and social media. An inattentive user clicks a link, thinks they are downloading a useful AI assistant, and gets malware instead.
How the attack works
The scheme is simple but effective. Scammers build websites that look almost identical to the original claude.com: the same logos, colors and text. But the domain name differs by one or two letters: claudde.com, claud3.com, or a lookalike that swaps in a Cyrillic letter for a Latin one. Such typos are easy to miss when you are in a hurry.
Links to the fake sites are spread through spam mailings, fake LinkedIn and Telegram accounts, and search results manipulated with SEO. The victim clicks and sees a nicely designed download page with a "Download installer" button. The file downloads, the user runs it, and a trojan is installed instead of Claude.
What is inside a fake installer
The contents depend on the attacker's skill. In simple cases it is an ordinary trojan that steals account credentials and passwords saved in the browser. In more sophisticated cases it is modular malware that can download additional components: spyware, a crypto miner, ransomware.
The danger lies in the disguise. While the malware runs in the background, the user sees a Claude installation window, waits a few minutes, and gets a success message. Everything looks normal. But malicious processes are already running, hidden, in the background.
- A trojan that steals passwords and cookies
- Spyware that logs keystrokes and takes screenshots
- A crypto miner that burns your PC's electricity
- A backdoor giving hackers remote access
- Ransomware that encrypts your files for a ransom
How to avoid getting caught
The main rule: download AI tools ONLY from official sources. For Claude, those are: the claude.ai web app (browser only, nothing to install), the mobile app from the App Store (iOS) or Google Play (Android), and the source code and API at github.com/anthropic-ai (for developers).
The second rule: don't skip checking the link before you click. Hover over the button and look at the bottom-left corner of the browser. What URL does it show? If it is not claude.ai or anthropic.com, don't click.
The third rule: pay attention to small details. Fake sites often give themselves away: typos in the Russian translation, odd design, no HTTPS (there will be no green padlock next to the address in the browser). The official claude.ai always uses a secure connection.
What this means
As AI tools grow more popular, so do attacks on their users. Scammers know people want to try Claude or ChatGPT, and they use that desire as bait to spread malware. So the best defense is attentiveness and a simple rule: links from social media and email are the enemy, the official website is a friend.
- Nov 2, 2026LLM Agent Built a Gearbox in KOMPAS-3D, but Scored Only 50 out of 100 on the Specification
- Nov 2, 2026Agents ignored the prompt to read memory in 7 of 7 sessions: an analysis of 13 thousand logs
- Nov 2, 2026Karpathy Built HackerTube, a Catalog of 6,454 Videos, in Two Hours with Claude Code
- Nov 2, 2026We Audited 929 Automations at Alpina: What Corporate AI Training Should Look Like in 2026
Key Questions Answered
How the attack works?
The scheme is simple but effective. Scammers build websites that look almost identical to the original claude.com: the same logos, colors and text. But the domain name differs by one or two letters: claudde.com, claud3.com, or a lookalike that swaps in a Cyrillic letter for a Latin one. Such typos are easy to miss when you are in a hurry. Links to the fake sites are spread through spam mailings, fake LinkedIn and Telegram accounts, and search results manipulated with SEO.
What is inside a fake installer?
The contents depend on the attacker's skill. In simple cases it is an ordinary trojan that steals account credentials and passwords saved in the browser. In more sophisticated cases it is modular malware that can download additional components: spyware, a crypto miner, ransomware. The danger lies in the disguise. While the malware runs in the background, the user sees a Claude installation window, waits a few minutes, and gets a success message. Everything looks normal.
How to avoid getting caught?
The main rule: download AI tools ONLY from official sources. For Claude, those are: the claude.ai web app (browser only, nothing to install), the mobile app from the App Store (iOS) or Google Play (Android), and the source code and API at github.com/anthropic-ai (for developers). The second rule: don't skip checking the link before you click. Hover over the button and look at the bottom-left corner of the browser. What URL does it show? If it is not claude.ai or anthropic.com, don't click.
Test Frontier LLMs & Autonomous Agents in One Workspace
Run Claude Opus 5.5, GPT-6, Gemini 3.1, and DeepSeek side-by-side in Nomad AI (nomadnet.ai) — unified model routing, deep research, and multimodal workflows under one subscription.
The AI world, distilled — once a week
Seven stories that actually mattered, hand-picked. No noise, no reposts, no press releases.
Done! Check your inbox for a confirmation.