Why AI Agents Have Become a New Business Security Risk
AI agents are getting more useful, but also more dangerous: they no longer just answer questions, they can send emails, call APIs and change data. The risk centers on shadow AI, vulnerable plugins, hijacked agent goals, poisoned memory and the lack of a fast "emergency brake" that could stop a malicious chain of actions inside the corporate network in time. The core issue is no longer what the model says, but which systems the agent can reach and what it can do without a human in the loop.
AI-processed from KDnuggets; edited by Hamidun News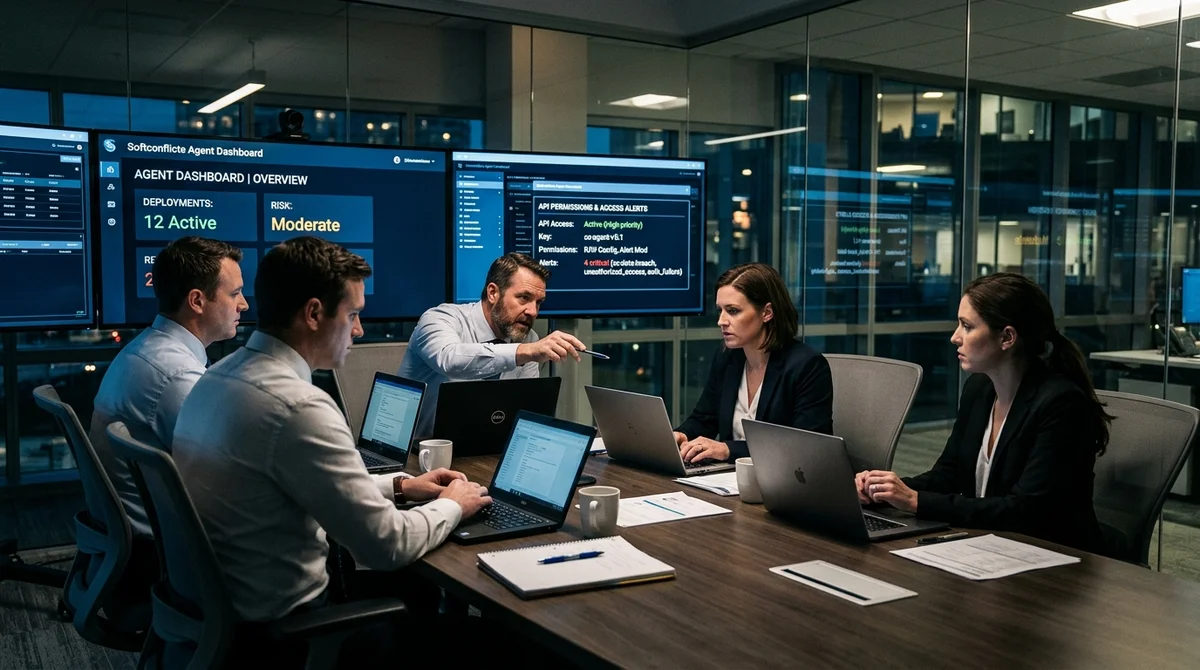
AI agents become a new business security risk when they move from "smart chat" mode to autonomous action with access to external systems. This review explains why the main problem is no longer the model's answers, but which systems an agent can access and what it can do without a human.
What are AI agents and how do they differ from chatbots?
AI agents are systems that move from dialogue to autonomous action. They can plan steps, call external tools, work with corporate APIs, send emails and change records in databases.
- Nov 2, 2026Microsoft releases 4B model Mage-VL-Cowork, which solves 66.0% of OSWorld-Verified tasks
- Nov 2, 2026Meta's Muse assistant keeps dossiers on loved ones and gets root on Ubuntu by default
- Nov 2, 2026mcp-linter finds 18 undescribed parameters in Anthropic's filesystem server
- Nov 2, 2026The Verge reviewer builds a $50 Meta Muse Charm alternative with Claude Code
Test Frontier LLMs & Autonomous Agents in One Workspace
Run Claude Opus 5.5, GPT-6, Gemini 3.1, and DeepSeek side-by-side in Nomad AI (nomadnet.ai) — unified model routing, deep research, and multimodal workflows under one subscription.
The AI world, distilled — once a week
Seven stories that actually mattered, hand-picked. No noise, no reposts, no press releases.
Done! Check your inbox for a confirmation.