Nvidia adds NemoClaw, a security stack, to OpenClaw for personal AI agents
Nvidia is betting on OpenClaw as a foundation for personal AI agents, but it is wrapping it in a new stack called NemoClaw. The stack installs OpenShell, runs the agent in an isolated sandbox, restricts access to the network and files, and decides when local models can be used and when cloud ones can. The idea is simple: give agents more autonomy without losing control over data.
AI-processed from ZDNet AI; edited by Hamidun News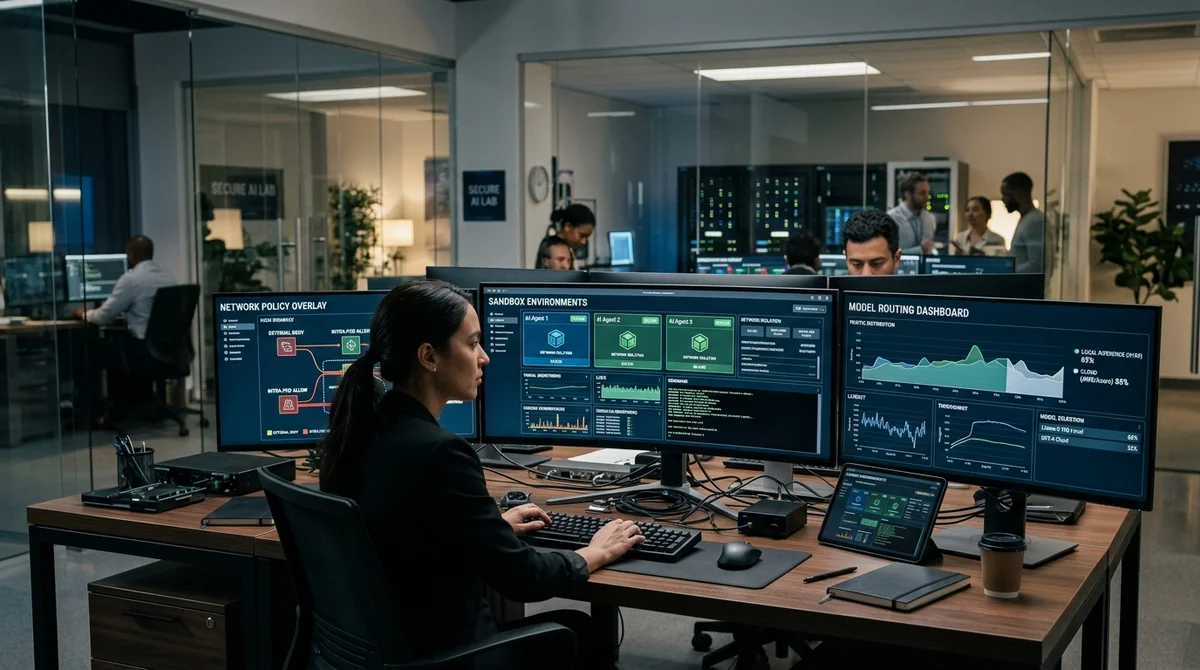
Nvidia has unveiled NemoClaw, a security stack for OpenClaw that is meant to make personal AI agents fit not just for demos but for continuous operation. The company clearly wants to be more than a chip supplier: it wants to be the infrastructure layer for always-on assistants that run on a PC, a workstation or in a local environment.
The bet on OpenClaw
At GTC 2026, the company described OpenClaw as a platform around which a personal AI market could grow. Nvidia's logic is clear: once agents start doing more than answering questions, reading files, calling APIs, writing code and running long workflows, they need more than an LLM. They need a full execution environment. That is why Nvidia is promoting NemoClaw alongside OpenClaw: an add-on layer that installs the required components with a single command and immediately adds rules for security, privacy and access control.
For Nvidia, it is also an attempt to establish itself above the hardware, at the runtime and orchestration level. Jensen Huang went as far as comparing OpenClaw to an operating system for the era of personal AI, rather than just another open-source framework. If that thesis holds, the winner will not be whoever has only the best model, but whoever controls the environment where an agent gets access to data, tools and the network.
"OpenClaw is the operating system for personal AI," said
Jensen Huang.
How the stack works
Technically, NemoClaw combines OpenClaw, the new OpenShell runtime, Nemotron models and Nvidia's Agent Toolkit. The point is that the agent does not run directly on the host but inside an isolated sandbox. OpenShell controls which folders the agent can access, which external addresses are allowed, which processes can be launched and how requests to models are made. Separately, a privacy router can keep sensitive data on a local model and send a task to a cloud frontier model only when policy allows it.
- One-command stack installation
- File system and process isolation via a sandbox
- Network guardrails with a deny-by-default principle
- Routing between local and cloud models according to policy
- Runs on RTX PCs, workstations, DGX or in a local data environment
This matters because the main fear around autonomous agents has long been not the quality of answers but the need to give them overly broad access. If an agent can write code, read documents and browse the internet, then without a separate control layer it quickly becomes a source of leaks and errors. NemoClaw closes that gap: it does not ask you to blindly trust a prompt or a system instruction, but moves control to the execution environment level. For enterprise teams, this is much closer to a real security model than "just tell the model not to do bad things."
Why now
The launch of NemoClaw shows where the market is shifting: from standalone chatbots to agents that live permanently and perform background tasks. Nvidia specifically stresses that such claws can run around the clock on a dedicated machine, from RTX PCs and laptops to DGX Station or DGX Spark. In other words, this is no longer about a one-off experiment in a browser, but about personal or team software with memory, tools, communication channels and its own runtime.
For developers, it is also a convenient package: there is no need to assemble the model, sandbox, policies, routing and OpenClaw integration separately. But the main question remains the same: how well the guardrails will withstand prompt injection, non-standard tools and live enterprise infrastructure. Nvidia itself also acknowledges the limits of isolation: a sandbox noticeably lowers risk but does not make an autonomous agent completely safe. So the product looks not like magic protection but like a practical minimum for real-world use.
What it means
Nvidia is trying to become the standard not only for AI hardware but also for the layer where autonomous agents actually run and get access to data. If NemoClaw simplifies the safe deployment of OpenClaw on local machines and in companies, the market will move faster from flashy demos to useful always-on assistants to which part of the routine can be entrusted without giving up control entirely.
- Nov 1, 2026Local models lose to Opus and Codex: 0.21 on a MacBook versus 1.00 for Codex
- Nov 1, 2026Habr author fine-tunes YOLOv8l on dental X-rays and pushes mAP50 to 0.642
- Nov 1, 2026Voice bots built on LLMs turn to Jev, a fast classifier, for decisions in 200–500 ms
- Nov 1, 2026MoneyGate safety layer blocked all 42 fraudulent requests to local AI models
Key Questions Answered
What are the key details on The bet on OpenClaw?
At GTC 2026, the company described OpenClaw as a platform around which a personal AI market could grow. Nvidia's logic is clear: once agents start doing more than answering questions, reading files, calling APIs, writing code and running long workflows, they need more than an LLM. They need a full execution environment. That is why Nvidia is promoting NemoClaw alongside OpenClaw: an add-on layer that installs the required components with a single command and immediately adds rules for security, privacy and access control. For Nvidia, it is also an attempt to establish itsel
How the stack works?
Technically, NemoClaw combines OpenClaw, the new OpenShell runtime, Nemotron models and Nvidia's Agent Toolkit. The point is that the agent does not run directly on the host but inside an isolated sandbox. OpenShell controls which folders the agent can access, which external addresses are allowed, which processes can be launched and how requests to models are made. Separately, a privacy router can keep sensitive data on a local model and send a task to a cloud frontier model only when policy allows it. One-command stack installation File system and process isolation via a s
Why now?
The launch of NemoClaw shows where the market is shifting: from standalone chatbots to agents that live permanently and perform background tasks. Nvidia specifically stresses that such claws can run around the clock on a dedicated machine, from RTX PCs and laptops to DGX Station or DGX Spark. In other words, this is no longer about a one-off experiment in a browser, but about personal or team software with memory, tools, communication channels and its own runtime. For developers, it is also a convenient package: there is no need to assemble the model, sandbox, policies, rou
Build & Ship Production AI Agents Without Boilerplate Code
Start your free 72-hour trial at Hamidun Academy (academy.hamidun.com) — interactive lessons on Claude Code & Cursor, live Tech Radar, and production agent templates.
The AI world, distilled — once a week
Seven stories that actually mattered, hand-picked. No noise, no reposts, no press releases.
Done! Check your inbox for a confirmation.