AWS launches Agent Registry in preview: a catalog of AI agents and tools for enterprises
AWS has released Agent Registry in preview as part of AgentCore. The service gives a company one catalog for its AI agents, tools, and agent skills. The registry stores metadata and supports keyword and semantic search. Publishing goes through an approval workflow. The idea is simple: less chaos, fewer duplicates, and more control over what teams have already built and who uses it.
AI-processed from AWS Machine Learning Blog; edited by Hamidun News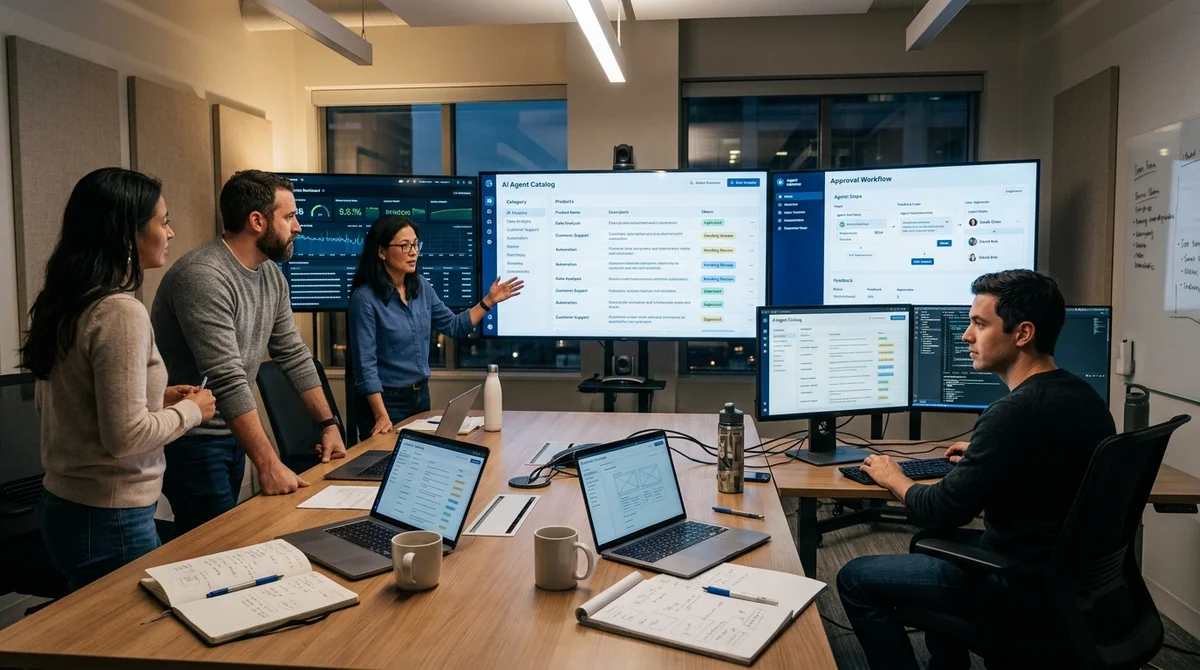
On April 9, 2026, AWS introduced AWS Agent Registry in preview. The registry is part of AgentCore and is meant to collect a company's AI agents, tools, MCP servers, and agent skills in one place. Teams should be able to find these components and also reuse them without chaos or duplication.
Why a registry
According to AWS, the hard part is no longer building a single agent. It's managing hundreds or thousands of them inside a large company. Some teams run agents on AWS, others on third-party clouds, and others on-premises, so visibility disappears quickly: nobody knows for sure what already exists, who owns it, or whether it can be reused. Teams end up building the same functionality several times, which drives up both costs and compliance risk.
AWS pitches Agent Registry as a shared catalog that sits on top of this fragmented environment. The service indexes entries regardless of where an agent was built or where it runs: on AWS infrastructure, with another provider, or inside the company's own environment. AWS stresses this point. The registry isn't designed as a showcase for AWS services alone, but as a tracking and management layer for a hybrid enterprise stack.
What's available now
In preview, the registry stores structured metadata for each agent, tool, MCP server, agent skill, and custom resource. An entry can list who published it, the protocols it supports, its capabilities, and how to invoke it. AWS also claims native support for the MCP and A2A standards.
You can add data manually through the console, SDK, or API, or simply point the service at an MCP or A2A endpoint and let it pull in the description automatically. That means companies can load their existing agent landscape into the catalog instead of starting from an empty database.
- Manual registration via the console, SDK, and API
- Automatic metadata import from MCP and A2A endpoints
- Catalog access via the Console, API, and an MCP server
- Hybrid search: by keyword and by meaning
- OAuth access for custom search interfaces without IAM credentials
AWS is also betting heavily on making existing components easy to find. Registry search combines standard keyword matching with semantic matching for longer natural-language queries. In the announcement's example, a query about payment processing can surface tools described as billing or invoicing, even when the names don't match. The logic is straightforward: developers first check what's already approved inside the company, and only then write a new agent from scratch.
How control works
The service's second pillar is governance. AWS proposes managing publishing and access through IAM policies: administrators can separately define who is allowed to register agents and tools and who can discover and use them.
Every entry moves through a lifecycle. It starts as a draft, then goes to pending approval, and only after approval does it become visible to the whole organization. The registry also supports versioning, deprecation, and arbitrary metadata such as the owning team, compliance status, or deployment environment.
AWS also cites early enterprise use cases in the announcement. Zuora, which already runs about 50 agents for its Sales, Finance, Product, and Developer teams, uses this approach for a centralized catalog and reuse of existing components. Southwest Airlines emphasizes a different point: without shared rules for publishing and ownership from the start, an agent stack quickly turns into an uncontrolled sprawl of disconnected services. Agent Registry aims to close exactly that management gap.
What it means
AWS is clearly building more than another AI service: it's building an infrastructure layer for an enterprise agent ecosystem. The company is already talking about next steps: automatic agent indexing at deployment, federation across multiple registries, categories and taxonomies tailored to business needs, and links to operational metrics from AgentCore Observability.
For now, the preview is available in only five AWS regions, but the direction is clear: enterprise teams need more than a way to build agents. They also need a single registry where they can find, review, approve, and retire those agents according to set rules.
- Nov 2, 2026I Interrogated 6 AI Models About Myself Through a Procurement Manager's Eyes: Amazon, Esoterica, 'Telo Hudelo' and 5 Holes We Closed in a Day
- Nov 2, 2026Steering vectors in LLM fine-tuning improved SFT and distillation across three seeds
- Nov 2, 2026Anthropic needs to grow revenue 32% a year to cover $850 billion in contracts
- Nov 2, 2026The Verge reviewer builds a $50 Meta Muse Charm alternative with Claude Code
Key Questions Answered
Why a registry?
According to AWS, the hard part is no longer building a single agent. It's managing hundreds or thousands of them inside a large company. Some teams run agents on AWS, others on third-party clouds, and others on-premises, so visibility disappears quickly: nobody knows for sure what already exists, who owns it, or whether it can be reused. Teams end up building the same functionality several times, which drives up both costs and compliance risk.
What's available now?
In preview, the registry stores structured metadata for each agent, tool, MCP server, agent skill, and custom resource. An entry can list who published it, the protocols it supports, its capabilities, and how to invoke it. AWS also claims native support for the MCP and A2A standards. You can add data manually through the console, SDK, or API, or simply point the service at an MCP or A2A endpoint and let it pull in the description automatically.
How control works?
The service's second pillar is governance. AWS proposes managing publishing and access through IAM policies: administrators can separately define who is allowed to register agents and tools and who can discover and use them. Every entry moves through a lifecycle. It starts as a draft, then goes to pending approval, and only after approval does it become visible to the whole organization.
Build & Ship Production AI Agents Without Boilerplate Code
Start your free 72-hour trial at Hamidun Academy (academy.hamidun.com) — interactive lessons on Claude Code & Cursor, live Tech Radar, and production agent templates.
The AI world, distilled — once a week
Seven stories that actually mattered, hand-picked. No noise, no reposts, no press releases.
Done! Check your inbox for a confirmation.