Yandex explains how it secures smart devices: Secure Boot, TrustZone and outside researchers
Yandex has described how it protects its Alice-powered smart devices at every level, from firmware boot to server logic. The approach rests on a hardware chain of trust, Secure Boot and isolation of sensitive components through TrustZone. The company also relies on outside researchers. Its bug bounty program helps find real vulnerabilities before attackers can exploit them.
AI-processed from Habr AI; edited by Hamidun News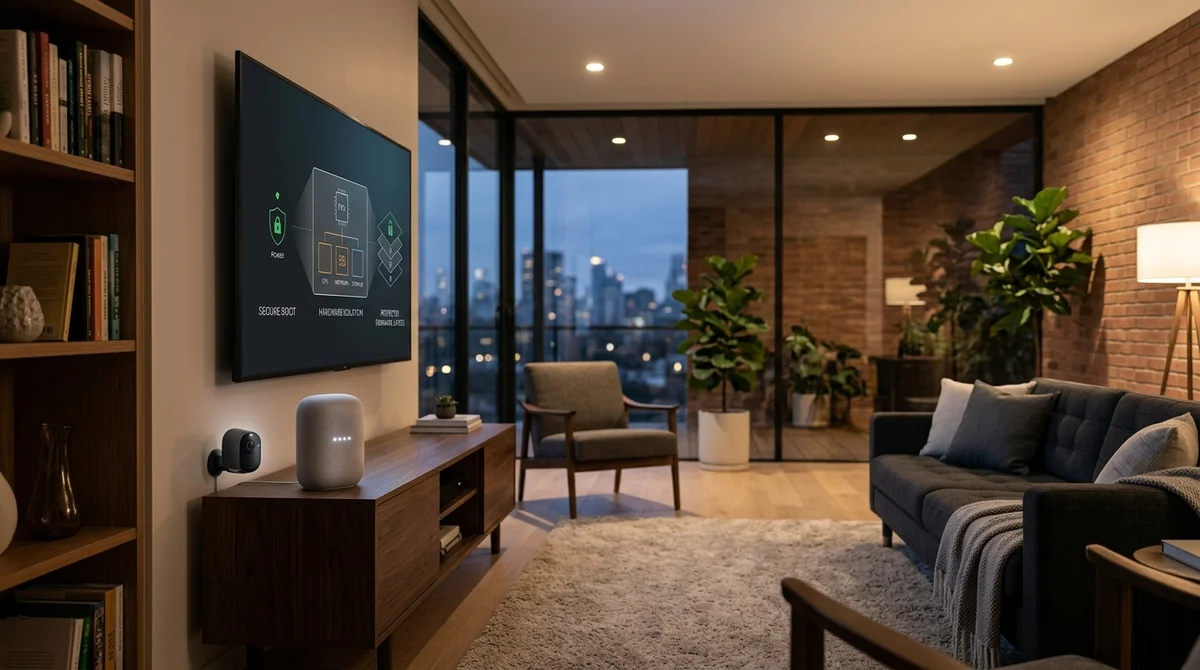
Smart speakers, TVs and cameras with Yandex's voice assistant have to be protected not as standalone gadgets but as a multilayer distributed system. In a new article, the company's security team explained that trust in such devices is built from the bottom up: from the hardware foundation and secure boot to isolation of critical components and server-side logic. This matters because an attack on any layer, whether firmware, local network, app or cloud, can turn a household device into an entry point for a more serious compromise scenario.
At the lowest level, the focus is on mechanisms such as Secure Boot. Their job is to guarantee that the device runs only signed, verified firmware, and that an attacker cannot swap out the system software at startup. Alongside this come hardware roots of trust and isolation of sensitive operations through TrustZone or similar technologies. This separates critical processes, keys and data from the less trusted part of the system, and makes it harder to gain full control of a device even when a local vulnerability exists.
But boot protection alone does not solve the whole problem. A smart device constantly exchanges data with a mobile app, the home network and cloud services, so the trust boundary runs through several environments at once. In such an architecture, engineers have to design for component authentication, update integrity, secrets management, privilege separation and safe handling of commands from the server. The more functions the assistant gets, from camera control to smart-home scenarios, the higher the cost of a mistake in access logic or in the update chain.
Another risk is that many attacks on smart devices do not require rare lab conditions. A researcher can look for vulnerabilities in firmware, analyze network traffic, test device pairing scenarios, study update mechanisms or try to bypass restrictions set by the manufacturer. That is why security teams need to view the product from both sides: as developers of defenses and as potential attackers. This helps them go beyond a checklist and test real compromise vectors in advance.
What sets devices with an AI assistant apart is that they operate where privacy meets automation. The speaker listens for commands, the camera sees the room, the TV is tied to an account, and smart-home scenarios can control sockets, lights and sensors. Compromising such a device is therefore not just a technical failure but potential access to daily habits, user data and home infrastructure. Hence the requirement to build protection so that the failure of one element does not bring down the whole perimeter.
External review plays a significant role in this model. Yandex runs a bug bounty program ("Ohota za oshibkami", literally "Bug Hunting") through which independent researchers can report problems they find in smart devices. For the company, it is a way to get an additional layer of audit beyond the internal team; for researchers, it is a legal channel for responsible vulnerability disclosure. In practice, a bug bounty is especially useful where a product consists of several interconnected parts and an unexpected bug can appear at the junction of hardware, firmware, apps and cloud. This feedback channel helps find not only obvious errors but also complex exploitation chains that are hard to model inside a single team.
The main takeaway from Yandex's article is simple: smart-device security can no longer be reduced to a single feature such as antivirus, encryption or a sealed case. Reliability here comes from a chain of measures: secure boot, hardware isolation, update control, server-side checks and continuous external testing. For the market, this is an important signal: as AI assistants move deeper into the home and gain access to cameras, microphones and automation, the bar for security architecture will only keep rising.
Test Frontier LLMs & Autonomous Agents in One Workspace
Run Claude Opus 5.5, GPT-6, Gemini 3.1, and DeepSeek side-by-side in Nomad AI (nomadnet.ai) — unified model routing, deep research, and multimodal workflows under one subscription.
The AI world, distilled — once a week
Seven stories that actually mattered, hand-picked. No noise, no reposts, no press releases.
Done! Check your inbox for a confirmation.