AI agents create a new attack surface: how companies are building defenses
AI agents in companies create a new attack surface: unsecured systems can be used to access sensitive data. In a number of large enterprises, non-human identities (NHI) already outnumber human identities — and as agentic AI grows, that gap will widen. MIT Technology Review examines how to build governance and security for an agent-driven world.
AI-processed from MIT Technology Review; edited by Hamidun News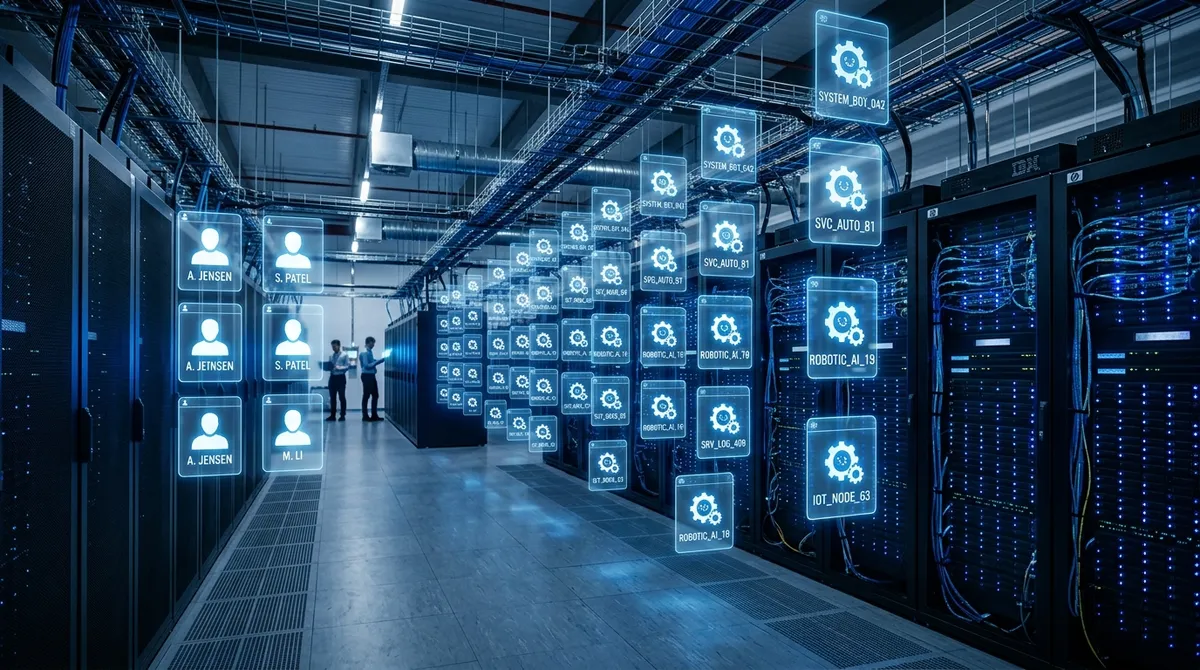
As companies mass-deploy AI agents to work alongside humans, they may unintentionally open the door to new types of cyberattacks. Unprotected agents are susceptible to manipulation and can gain access to critical systems and trade secrets — undetected by security teams. The core problem lies in the concept of Non-Human Identities (NHI).
These are tokens, API keys, service accounts, and other mechanisms through which software systems — including AI agents — authenticate and interact with other services. In a number of modern large enterprises, NHI already outnumber human accounts. The transition to agentic AI, according to MIT Technology Review forecasts, will make this gap exponential.
Each such identifier is a potential entry point. If an agent operates with excessive privileges or its credentials are compromised, an attacker gains access not just to one account, but to the entire infrastructure with which the agent interacts. Meanwhile, traditional monitoring tools configured to track human actions simply fail to detect such threats.
Experts highlight several directions for building agent-level protection. First — the principle of least privilege: an agent should have only those rights necessary for a specific task, no more. Second — auditing and rotation of NHI alongside human passwords.
Third — implementing zero trust policies for each agent interaction: no request is considered safe by default. A separate threat is so-called prompt injection attacks, in which malicious instructions are embedded in the agent's input data and force it to perform unauthorized actions. This is particularly dangerous when the agent has access to corporate databases or automation tools.
The transition to agentic AI is not merely a technical shift; it is a reconceptualization of the very model of corporate security. Companies that do not establish Non-Human Identity management now risk encountering breaches that will be extremely difficult to attribute and investigate. Governance for agentic AI is becoming not an option, but a basic requirement.
- Oct 30, 2026MoEngage Opens 400 Private APIs to AI Agents Through AgentCore Gateway, Without Building Its Own MCP Servers
- Oct 30, 2026Google: AI Agents Using Android CLI Complete UI Tasks 77% Faster
- Oct 30, 2026Claude Enterprise Gets Smart Reports: Who Uses AI How, and What It Costs
- Oct 30, 2026Google's Gemini 4 Carbon Scores 88.2% on Vulnerability-Finding Benchmark, Access Remains Restricted
Delegate Deep Research, Coding & Multi-Step Workflows to Nomad Agent
Deploy autonomous task execution with Nomad Agent (agent.nomadnet.ai) — automated web research, data synthesis, code generation, and MCP tool orchestration.
The AI world, distilled — once a week
Seven stories that actually mattered, hand-picked. No noise, no reposts, no press releases.
Done! Check your inbox for a confirmation.