Code Security Without YAML: How GitLab Scales Scanning
GitLab 19.0 lets teams enable SAST, dependency scanning, and secret detection across all projects at once instead of configuring each file by hand. You create a security configuration profile at the group level and apply it to every project in one click. Scans run automatically whenever a merge request is opened and whenever changes are merged into the default branch.
AI-processed from GitLab Blog; edited by Hamidun News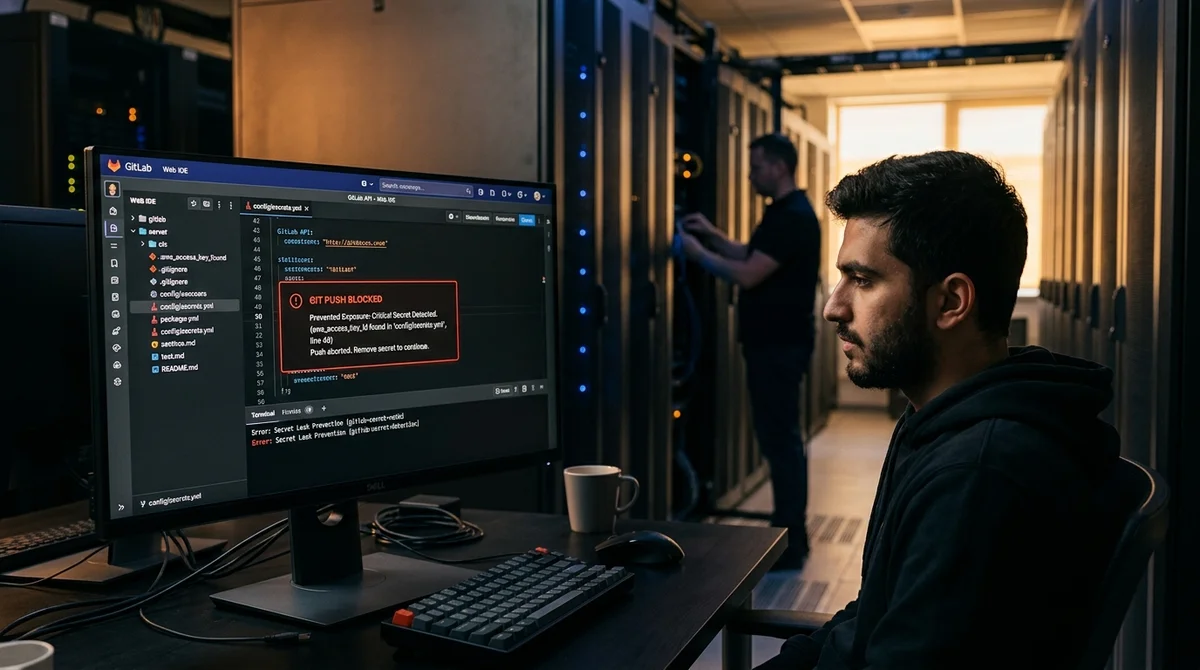

As an organization grows, configuring security scanners by hand for every project becomes unmanageable. GitLab 19.0 addresses this with security configuration profiles, which let you enable SAST, dependency scanning, and secret detection for all projects at once in a single click, with no need to edit YAML files.
Why manual configuration doesn't scale
Early on, manual setup works fine: one team, a handful of repositories, and one security engineer who knows everything by heart. But as the number of teams and projects grows, the model starts to fall apart. AI speeds up development, but security coverage falls behind even faster.
The problems are familiar and painful. Teams copy scanning configuration from wherever they can find it, so SAST runs with one ruleset in a backend service and a completely different one in the frontend. Dependency scanning gets added to new projects but never to old ones.
Someone edits .gitlab-ci.yml to fix a pipeline error, accidentally removes a security scanner, and nobody notices until an incident.
Without centralized management, there is no way to confirm that every project follows the same security policy. The security team has to check each project by hand and chase down configuration instead of focusing on analyzing real vulnerabilities.
What configuration profiles are A configuration profile is a set of
rules and triggers that define how and when security scanners run. Instead of hand-editing .gitlab-ci.
yml in every project, you create a profile once at the group level and apply it to all projects in a single action. GitLab ships ready-made profiles for three scanner types: SAST (Static Application Security Testing) — finds vulnerabilities in application source code Dependency scanning — detects vulnerabilities in the libraries and packages you use * Secret detection — catches API keys, passwords, and tokens before they reach the repository Each profile contains vetted, recommended settings that follow industry best practices. That means you can turn on full security scanning in minutes without writing a single line of YAML and without deep knowledge of each scanner.
How scan triggers work Scans run automatically in three scenarios.
First, when a merge request is created. The scanner shows only the new vulnerabilities introduced in that code, so developers can focus on their own mistakes instead of getting distracted by older issues that predate their pull request. Second, when changes are merged into the default branch. The security team then sees the full security picture of the entire codebase and can track how it improves over time. Third, secret detection runs in real time. If a developer tries to push an API key or password, the push is blocked right at the git level before the secret reaches the repository and its commit history. This prevents situations where secrets end up in public history and require costly rotation.
From zero to full coverage in a few clicks
To get started, the security team opens their group's Security inventory, selects all projects (or specific ones), and applies the default profiles through the Bulk Actions menu. GitLab immediately shows coverage status: a green bar means the scanner is fully active, a partial bar means not all triggers are working, and a gray bar means the scanner isn't configured yet. The ready-made profiles take effect immediately. The first scan runs on the next merge request or push to the default branch.
What it means Organizations no longer have to choose between development speed and security.
Configuration profiles let them scale both at once: teams ship new code faster while every project is guaranteed to go through the same set of critical security checks. This matters most in large organizations, where development runs in parallel across dozens or hundreds of projects at the same time.
- Oct 31, 2026Author puts his script before an AI jury: the verdict cost 850 thousand tokens
- Oct 29, 2026OvisOCR3: an 0.8B-parameter model that reads documents better than specialized systems
- Oct 29, 2026Tencent releases Youtu-Parsing-Omni: one model parses documents, audio and video
- Oct 28, 2026Liquid AI releases LFM2.5-24B-A2B: an agent model with 2B active parameters
Test Frontier LLMs & Autonomous Agents in One Workspace
Run Claude Opus 5.5, GPT-6, Gemini 3.1, and DeepSeek side-by-side in Nomad AI (nomadnet.ai) — unified model routing, deep research, and multimodal workflows under one subscription.
The AI world, distilled — once a week
Seven stories that actually mattered, hand-picked. No noise, no reposts, no press releases.
Done! Check your inbox for a confirmation.