How LangChain Keeps Credentials Away From Agents in LangSmith
LangChain has added Auth Proxy to LangSmith Sandboxes, a new security layer that hides API keys from the agents themselves and limits their network access. It filters outbound connections by domain, stores credentials at the infrastructure level and audits every request. The company says developers get full control over what their agents can connect to.
AI-processed from LangChain Blog; edited by Hamidun News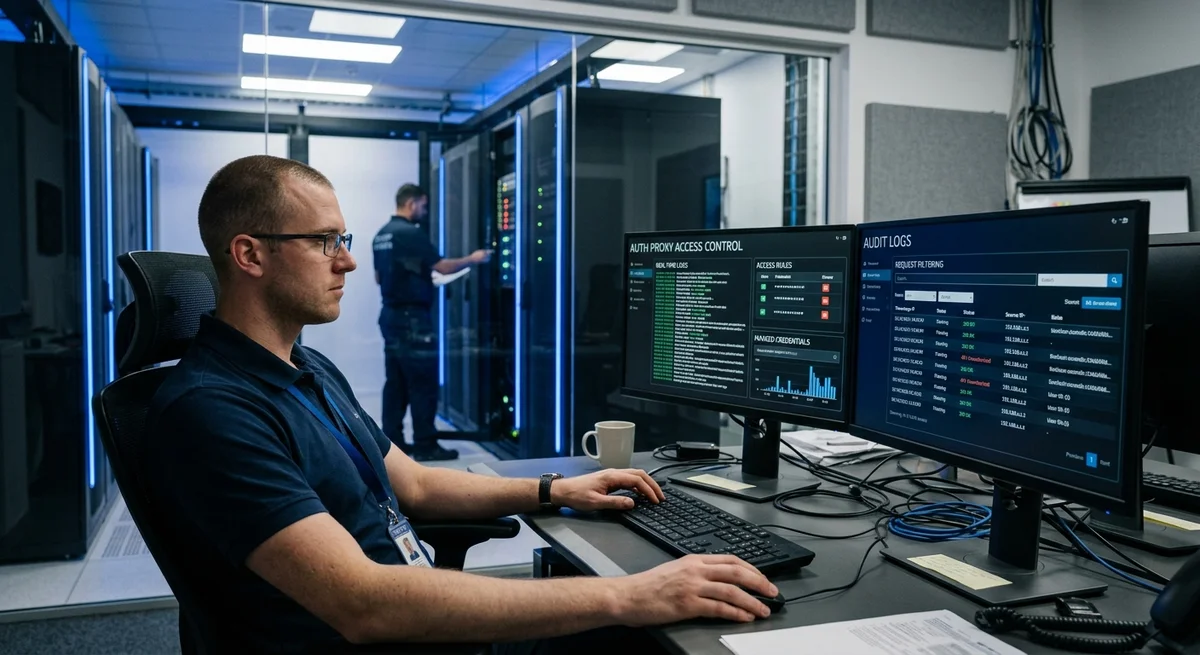
LangChain has updated LangSmith Sandboxes with Auth Proxy, an access-control system for AI agents. Credentials are now invisible to the agents themselves, and outbound connections are controlled at the infrastructure level.
The agent security problem
AI agents have to work with the real world: call APIs, make HTTP requests, connect to databases. For that they need API keys, passwords and other credentials. But if an agent is compromised, whether by a bug in the code or a malicious instruction in a prompt, it can steal that data and use it for unauthorized access. A single leaked Admin API key can lead to a breach of the entire system.
Until now, developers had to hand keys to the agent and hope it would not steal them.
How Auth Proxy works
Auth Proxy sits as an intermediate layer between the agent and external services. All credentials are now stored at the infrastructure level, not in the agent's code or environment variables.
When an agent wants to call an API, the request goes through Auth Proxy. The system checks it, applies access rules, inserts the required credentials and lets the connection through.
Auth Proxy features:
- Hides API keys from agent code
- Filters outbound connections by domain and IP address
- Audits all requests that use credentials
- Flexible access rules managed by the team
- Integration with secrets-management systems (AWS Secrets Manager, Vault)
Infrastructure control instead of code control
The key difference with Auth Proxy is that control now lives in the infrastructure, not in the code. Previously, the developer decided what data to send to the agent. Now the security team can set rules such as "this agent can only call the payments API," "all connections go through a VPN," or "requests require manual approval."
Changing the rules does not require rewriting or recompiling code; updating the configuration in the LangSmith Dashboard is enough.
A practical example
Imagine an agent that orders goods through a supplier's API. It needs the supplier's key and a payment system key. Previously, both keys were passed into the agent's environment variables, so if the agent was hacked, both were compromised.
Now Auth Proxy acts as the intermediary: the agent simply says "order the item." Auth Proxy checks whether that is allowed and inserts the required keys into the request itself. If needed, the system logs all operations and requires manual approval.
What this means
Auth Proxy makes LangSmith safer for commercial and critical applications. Companies will be able to deploy AI agents in production without fear of credential leaks. This matters especially for payment operations, cloud infrastructure management and access to customers' private data.
- Oct 31, 2026Worldwide Express hands disputed invoices to AI agents and cuts unresolved disputes by 75%
- Oct 30, 2026AWS gives coding agents a live site preview straight from an isolated session
- Oct 30, 2026MoEngage Opens 400 Private APIs to AI Agents Through AgentCore Gateway, Without Building Its Own MCP Servers
- Oct 29, 2026NVIDIA Nemotron 3.5 Super VL: 120B Parameters, 12B Active, Running on AWS
Key Questions Answered
What are the key details on The agent security problem?
AI agents have to work with the real world: call APIs, make HTTP requests, connect to databases. For that they need API keys, passwords and other credentials. But if an agent is compromised, whether by a bug in the code or a malicious instruction in a prompt, it can steal that data and use it for unauthorized access. A single leaked Admin API key can lead to a breach of the entire system. Until now, developers had to hand keys to the agent and hope it would not steal them.
How Auth Proxy works?
Auth Proxy sits as an intermediate layer between the agent and external services. All credentials are now stored at the infrastructure level, not in the agent's code or environment variables. When an agent wants to call an API, the request goes through Auth Proxy. The system checks it, applies access rules, inserts the required credentials and lets the connection through. Auth Proxy features: Hides API keys from agent code Filters outbound connections by domain and IP address Audits all requests that use credentials Flexible access rules managed by the team Integration with
What are the key details on Infrastructure control instead of code control?
The key difference with Auth Proxy is that control now lives in the infrastructure, not in the code. Previously, the developer decided what data to send to the agent. Now the security team can set rules such as "this agent can only call the payments API," "all connections go through a VPN," or "requests require manual approval." Changing the rules does not require rewriting or recompiling code; updating the configuration in the LangSmith Dashboard is enough.
Test Frontier LLMs & Autonomous Agents in One Workspace
Run Claude Opus 5.5, GPT-6, Gemini 3.1, and DeepSeek side-by-side in Nomad AI (nomadnet.ai) — unified model routing, deep research, and multimodal workflows under one subscription.
The AI world, distilled — once a week
Seven stories that actually mattered, hand-picked. No noise, no reposts, no press releases.
Done! Check your inbox for a confirmation.